
Firewall management
Your firewall is delivering half of what you paid for
Review and support of what is already installed, or a perimeter built from scratch. Rules nobody reviews, logs that go nowhere, inspection switched off by an expired certificate.
The problem
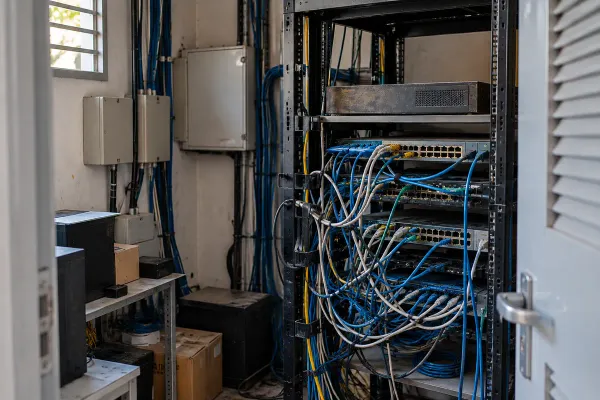
The appliance was bought at a high price and configured once. Two years later there are broad rules nobody remembers creating, logs never reach the SIEM, and features the license charges for are switched off.
In action
See it happen
- Rules by application
- Zones and profiles
- Policy test
- Application blocked
In practice
Where this is already running
-
 Client: Grupo NTK Over seven years of IT modernization and automation, NTK cut its monthly IT tickets by 42%. Today, an AI agent handles requests by chat. See the case
-
 Client: FS Logistics Virtualized infrastructure, a domain controller and a Next Generation Firewall with strict rules: FS Logistics met the security criteria and obtained its Siscomex registration. See the case
-
 Client: Diniz Angelo A file server with access policies, accounts managed in one place and a Next Generation Firewall at the edge: Diniz Angelo’s documents moved off the lawyers’ computers. See the case
What you get
What ends up running in your environment
- A perimeter built from scratch when there is none yet: firewall, rules and VPN
- Rule review: what is used, what is too broad, and what never matched anything
- Segmentation designed around what the company actually does
- Logs reaching detection, which is what makes a firewall useful after the incident
- VPN with a second factor, including for administrative access
- DNS and URL filtering, at both layers
What you should know first
We work on the equipment you already own, or build the perimeter from scratch on the equipment your company buys. We do not sell firewalls or run penetration tests.
The firewall you already paid for, working in full: rules reviewed and logs going where they should.